
Scan from your terminal,
or your CI pipeline.
@scanverra/cli scans secrets, SAST issues, dependency CVEs, IaC misconfigurations and quality issues on your own machine. No GitHub or Bitbucket connection needed, and only the findings are sent to Scanverra.
Requires Node.js 18 or newer and a Scanverra API key. The Free plan includes one.
Read the quick start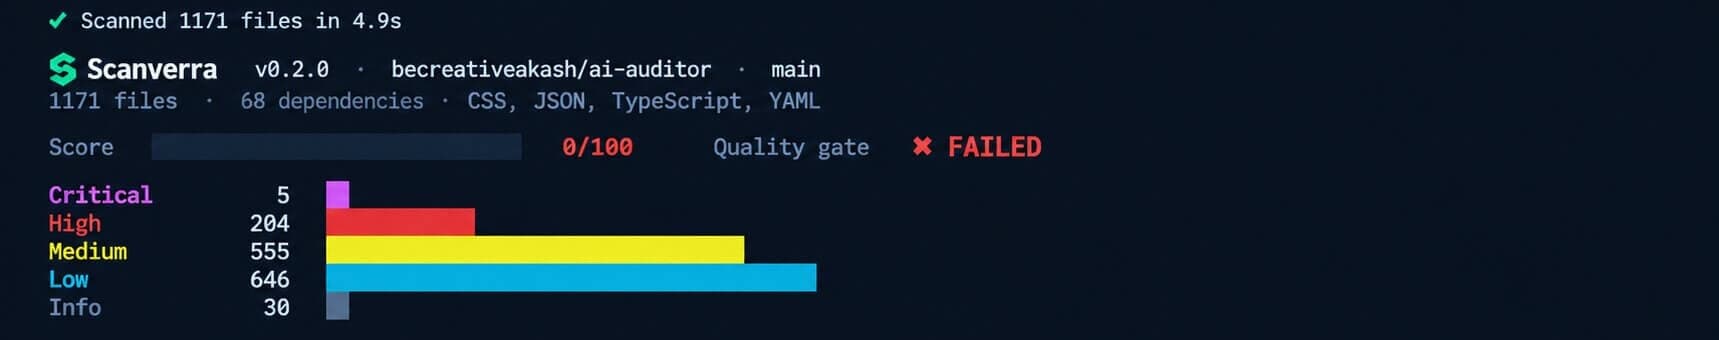
Built for the terminal and CI
The same checks as the dashboard, run wherever your code already is.
Runs anywhere
One command in any shell, any CI runner, or a pre-commit hook. No account connection or OAuth to set up first.
CI-native output
SARIF for GitHub code scanning and Sonar import, JSON for custom tooling, and exit codes to gate a build with --fail-on.
Same engine as the dashboard
Secrets, SAST, dependency CVEs, IaC and quality checks. Results match a scan started from Scanverra, wherever you run it.
Filter what you gate on
Focus a build check on security and dependency findings with --category, and leave quality opinions out of CI.
How it works
From install to a result in your dashboard.
Install or run once
npx @scanverra/cli, or npm i -g @scanverra/cli for a permanent scanverra command.
Log in
Paste an API key once. In CI, set SCANVERRA_API_KEY as a secret instead.
Scan
scanverra scan . reads your files, runs the checks locally, and prints the results.
Review or gate
Open the link in your dashboard, or let --fail-on stop the build on a real problem.
Add it to GitHub Actions
Scan every push and pull request, fail the job on high-severity findings, and see results in GitHub code scanning.
on: [push, pull_request]
jobs:
  scanverra:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      security-events: write
    steps:
      - uses: actions/checkout@v7
      - uses: scanverra/scan-action@v1
        with:
          api-key: ${{ secrets.SCANVERRA_API_KEY }}
          fail-on: high
Store your API key as the SCANVERRA_API_KEY repository secret. Any other CI works with npx @scanverra/cli scan . --fail-on high.
What leaves your machine
Uploaded
- File paths and line numbers
- Rule IDs, titles, severities and fix suggestions
- Dependency names and versions
- Project, branch and commit
Never uploaded
- File contents
- Secret values
- The matched line of code (unless you pass --include-code)
Full check list
Everything the web scanner checks, available from the command line.
Related reading
Automating Code Quality and Dependency Audits in CI/CD
How to catch vulnerable dependencies, license issues, and quality drift on every pull request instead of during a quarterly cleanup.
npm audit vs. Snyk vs. Dependabot: Choosing the Right Dependency Scanner
Three names that come up constantly, doing genuinely different jobs - and why most teams end up using more than one, not choosing just one.
Understanding CVSS Scores: How to Prioritize Vulnerability Fixes
A 9.8 and a 7.5 aren't just "high" and "medium" - what actually goes into a CVSS score, and why the number alone shouldn't decide what you patch first.
Scanverra for VS Code
See findings inline while you code
Repo Scanner
Code quality & dependency health
Security Scanner
Headers, secrets, SSL & CSRF risk
Website Audit
Performance, SEO & accessibility
Add it to your pipeline today
One command, no repo connection, and your code never leaves the runner.